As industries become more digitally connected, the gap between Information Technology (IT) and Operational Technology (OT) continues to close. While this brings incredible efficiency, it also opens up critical industrial systems to serious cyber risks. Unlike an IT crash that might simply pause email access, an outage in an OT network—like a power grid, water treatment plant, or manufacturing line—can have severe physical, financial, and safety consequences.
To secure these highly sensitive environments without causing disruptions, organizations are turning to Passive OT Network Monitoring. Here’s a breakdown of what it is, how it works, and why it is indispensable for modern industrial security.
What is Passive OT Network Monitoring?
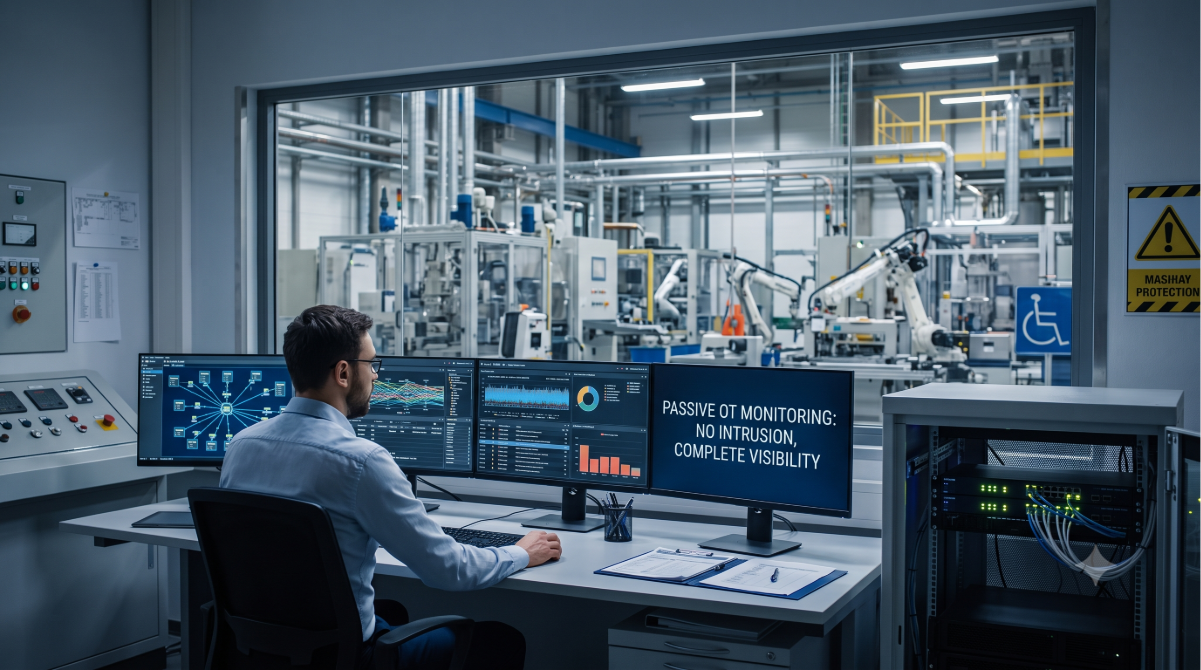
Passive OT network monitoring is a non-intrusive method of observing and analyzing industrial network traffic to identify assets, assess vulnerabilities, and detect cybersecurity threats.
Unlike Active Monitoring, which sends query packets directly to devices to retrieve information (a practice that can crash fragile, older industrial controllers), Passive Monitoring takes a completely “hands-off” approach.
It acts as an invisible observer. By utilizing network TAPs (Test Access Points) or SPAN (Switch Port Analyzer) ports, a passive sensor captures a copy—or mirror—of the data already flowing through the network. The sensor reads this mirrored data out-of-band, ensuring that the monitoring system never injects packets, introduces latency, or directly interacts with the active, physical control devices.
How It Works: “The Truth is in the Packet”
Because industrial devices communicate constantly to run operations, they reveal a vast amount of information naturally. Through Deep Packet Inspection (DPI) of the copied traffic, passive monitoring systems can:
-
Discover Assets: Automatically identify every connected device (PLCs, HMIs, sensors) based on its natural communication behavior, vendor signatures, and protocols.
-
Map Network Topology: Build a visual map of how devices communicate, identifying which systems talk to one another and finding unauthorized connections.
-
Establish Operational Baselines: Understand what “normal” looks like on a daily basis (e.g., standard times, expected commands, typical bandwidth).
-
Spot Anomalies: Flag unusual behaviors in real-time, such as a controller receiving an unrecognized command or communicating with an external IP address for the first time.
Why Passive OT Network Monitoring Matters
For decades, many OT environments relied on air-gapped security—the assumption that being disconnected from the internet kept them safe. Today, that is no longer enough. Here is why passive monitoring has become the gold standard for securing these networks:
1. Uptime is Non-Negotiable
In OT, availability is the top priority. Many Industrial Control Systems (ICS) are extremely sensitive and run on legacy protocols (like Modbus or DNP3) that were never designed with security or heavy traffic in mind. An active query or a misplaced scan can easily overload these systems, causing physical shutdowns. Passive monitoring eliminates this risk entirely, collecting crucial safety data while keeping production running smoothly.
2. You Can’t Protect What You Can’t See
Many industrial plants have grown incrementally over decades, leading to a lack of accurate device inventories. Passive monitoring instantly creates a real-time, continuous inventory of all hardware, software, firmware, and connections. It uncovers “shadow OT”—devices plugged in by operators or third-party contractors that security teams didn’t know existed.
3. Legacy-Friendly Security
Older OT devices often cannot run modern security agents. In fact, attempting to install software on them can void warranties or break certifications. Because passive monitoring happens at the network layer via TAPs, it can monitor even the oldest, most delicate legacy assets without needing to touch or reconfigure them.
4. Early Detection of Cyber Threats and Human Error
Cybercriminals frequently target industrial sectors, hoping to disrupt critical infrastructure. Passive monitoring helps teams spot early warning signs of an attack, such as lateral movement or reconnaissance. Just as importantly, it detects human error—like an operator loading incorrect firmware or changing a configuration at an unauthorized time.
5. Safe Vulnerability Management
Knowing which devices have unpatched vulnerabilities is vital. Passive monitoring identifies these vulnerabilities by matching observed device signatures and firmware versions against known vulnerability databases. This allows security teams to assess risk without ever having to run intrusive, risky scans on active machinery.
Conclusion
In the industrial world, safety and continuous operation are paramount. Trying to force IT-style active scanning on brittle, high-stakes OT environments is a recipe for disaster.
Passive OT Network Monitoring bridges this gap perfectly. By listening without interrupting, it gives security and operations teams the deep visibility, threat detection, and asset awareness they need—all while ensuring that the physical systems keeping our world moving never miss a beat.