Operational Technology (OT) and Cyber-Physical Systems (CPS) power modern industrial infrastructure, including manufacturing lines, energy grids, and water processing facilities. Historically, these environments relied on physical air-gapping for protection. Today, digital transformation demands continuous connectivity for real-time monitoring, emergency troubleshooting, and third-party vendor maintenance.
Traditional remote access mechanisms—such as generic virtual private networks (VPNs) and IT jump servers—often fall short in industrial settings. They frequently grant overly broad network permissions, lack visibility into proprietary industrial protocols, and create security blind spots. Claroty Secure Remote Access (SRA)—part of the Claroty xDome ecosystem—addresses these challenges with an architecture specifically built for OT environments.
Core Capabilities & Architecture
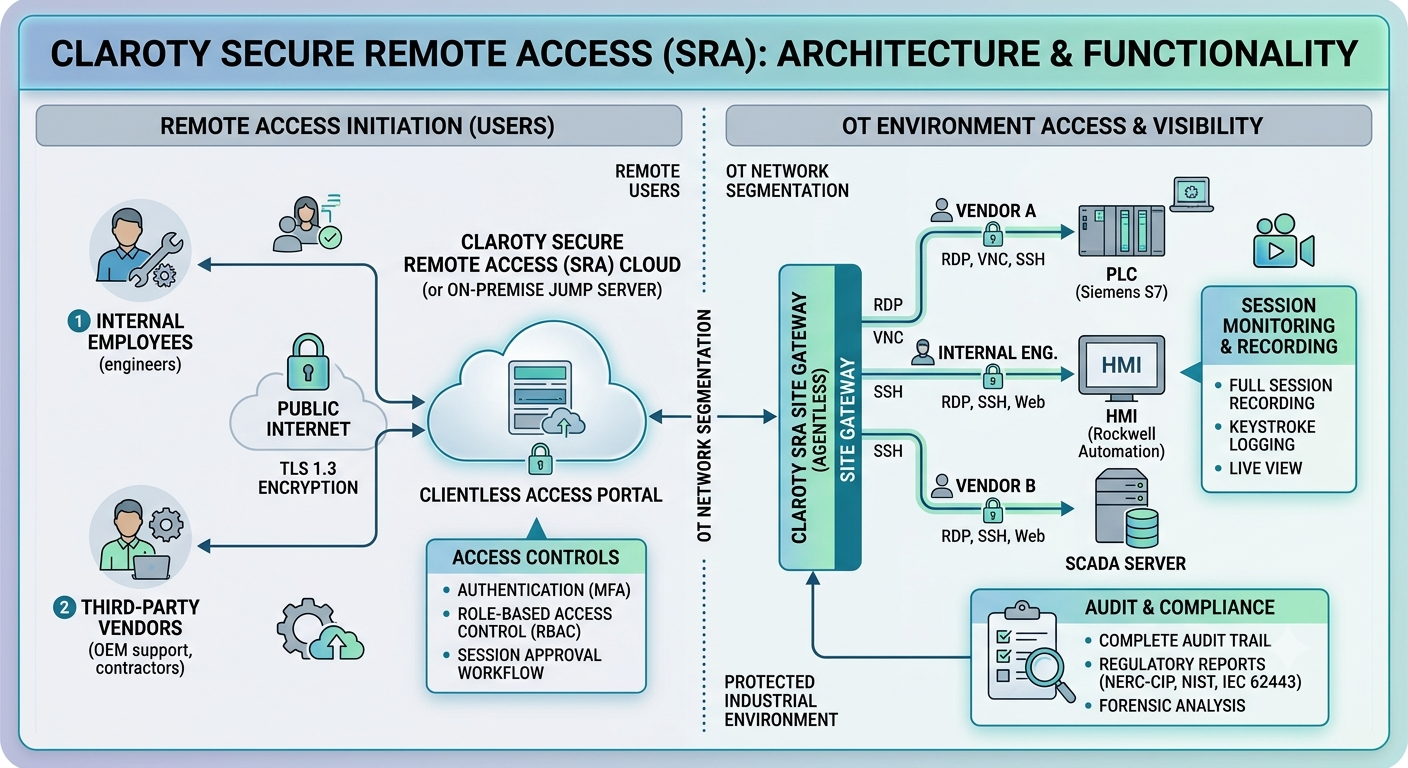
Claroty SRA implements a Zero Trust Network Access (ZTNA) framework to secure interactions between remote users and critical physical infrastructure.
| Operational Focus | Technical Capability | Security Benefit |
| Authentication & Identity | Multi-Factor Authentication (MFA) & IAM Integration | Mitigates credential theft and unauthorized access attempts. |
| Access Control | Granular Role-Based Access Control (RBAC) | Restricts user permissions to specific devices (e.g., PLCs, HMIs) rather than open network segments. |
| Session Control | On-Demand Approval & Emergency Access Workflows | Ensures local plant engineers maintain oversight of third-party vendor activities. |
| Audit & Governance | High-Definition Session Recording & Keystroke Logs | Delivers complete visibility and forensic readiness for compliance standards like NIST and IEC 62443. |
| Architecture Flexibility | Clientless Web Access / Hybrid Deployment Options | Works via standard browsers without client installation; supports cloud-managed and edge-gateway deployments. |
Mitigating Third-Party and System Risks
Industrial environments frequently require specialized original equipment manufacturer (OEM) support and third-party contractors. Unmonitored vendor connections introduce significant risks, such as rogue configuration updates or unpatched software exposure. Claroty SRA establishes secure, agentless access portals that enforce least-privilege policies.
By isolating remote sessions through dedicated SRA gateways, the platform prevents lateral movement across plant zones. Security teams can perform over-the-shoulder monitoring during active connections, giving them the ability to terminate suspicious sessions instantly before operational disruptions occur.
Operational Resilience
Claroty SRA bridges the gap between IT security policies and plant operational needs. Its low-bandwidth design supports remote, geographically distributed facilities while preserving uptime. By centralizing identity governance, eliminating “shadow” access tools, and simplifying audit logging, Claroty SRA allows industrial enterprises to scale remote operations securely.